EnvChain
v1.1.0Replace .env files, key files, and certificates with an encrypted vault that injects them on demand.
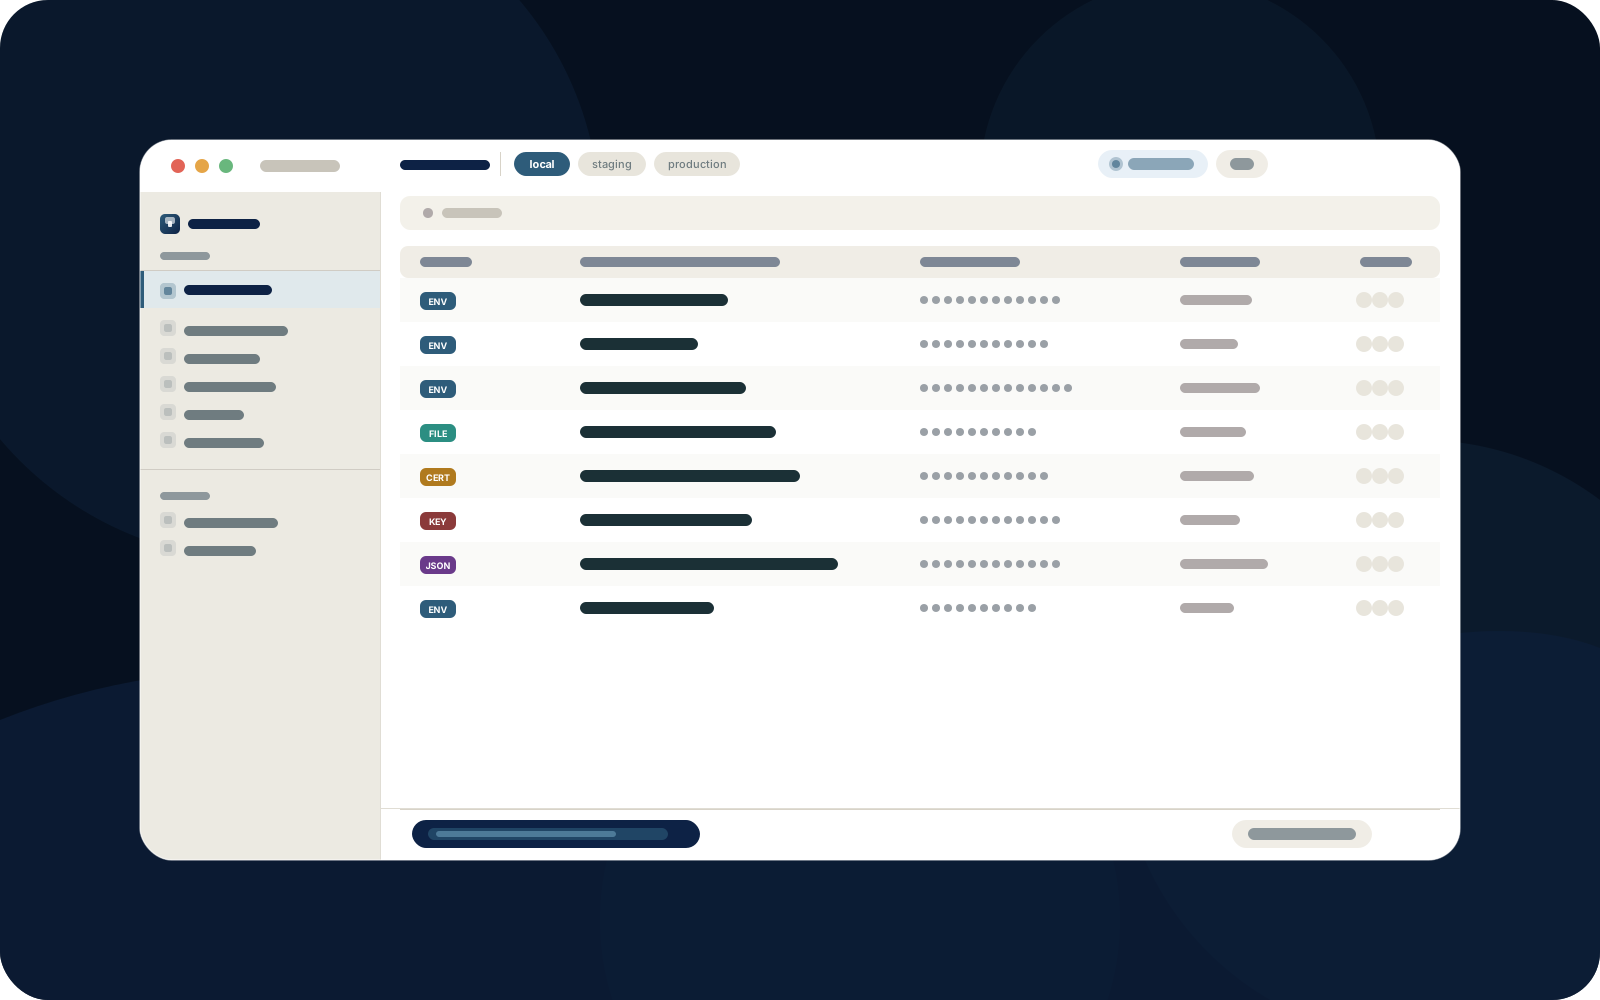
EnvChain replaces the loose .env files, .pem certificates, signing keys, and service-account JSON that pile up in plaintext on dev machines. Sensitive items live in a single encrypted local vault unlocked with Touch ID. Run `envchain run -- npm start` to inject secrets straight into a process without writing them to disk, or drop a `.envchain` marker into a project so tools that read .env directly (Vite, Next.js, Docker Compose) keep working against a temporary 0600 file that auto-shreds when the build exits. Every read, export, and team-sync event lands in a local audit log.
Built for more than env vars
Store env-var secrets, .env files, .pem certificate chains, signing keys, and service-account JSON side by side. Plaintext copies on disk become opt-in, not the default.
Encrypted local vault
Everything sensitive lives in one encrypted vault on your Mac. Nothing leaves the device unless you explicitly export a sealed bundle.
Touch ID unlock
Unlock with Touch ID instead of retyping a master password every time you open a project.
Inject without writing files
`envchain run -- <cmd>` injects secrets as process-scoped env vars. Virtual .env mode keeps Vite, Next.js, dotenv-cli, and Docker Compose working against a temporary 0600 file that auto-shreds on exit.
Shell hook and SDKs
A direnv-style shell hook auto-loads the right environment when you cd into a project. Node, Python, and Go SDKs pull secrets straight into your runtime.
Team sync and audit log
Share sealed bundles with teammates through any channel; recipients decrypt locally. Every read, export, and sync is appended to a local audit log.